Хочете будувати кар’єру в Data Science та AI? Vodafone Big Data Lab відкриває новий набір —>
Олег ОнопрієнкоHot News
11 November 2026, 12:20
2026-11-11
"Get up, Donbass" from the children's room. How hackers break into Ukrainians' home cameras and how to protect your home
Ukrainians are increasingly facing hacking of home surveillance cameras. Unknown people gain remote access to devices, monitor private lives, control lenses and even turn on Russian propaganda in the middle of the night. The extremely popular in Ukraine Dahua brand equipment has been at risk. We tell you how this hacking scheme works, what security companies say and how to permanently block attackers from accessing your video stream.
Ukrainians are increasingly facing hacking of home surveillance cameras. Unknown people gain remote access to devices, monitor private lives, control lenses and even turn on Russian propaganda in the middle of the night. The extremely popular in Ukraine Dahua brand equipment has been at risk. We tell you how this hacking scheme works, what security companies say and how to permanently block attackers from accessing your video stream.
A wave of hacks and the Russian anthem instead of an alarm clock
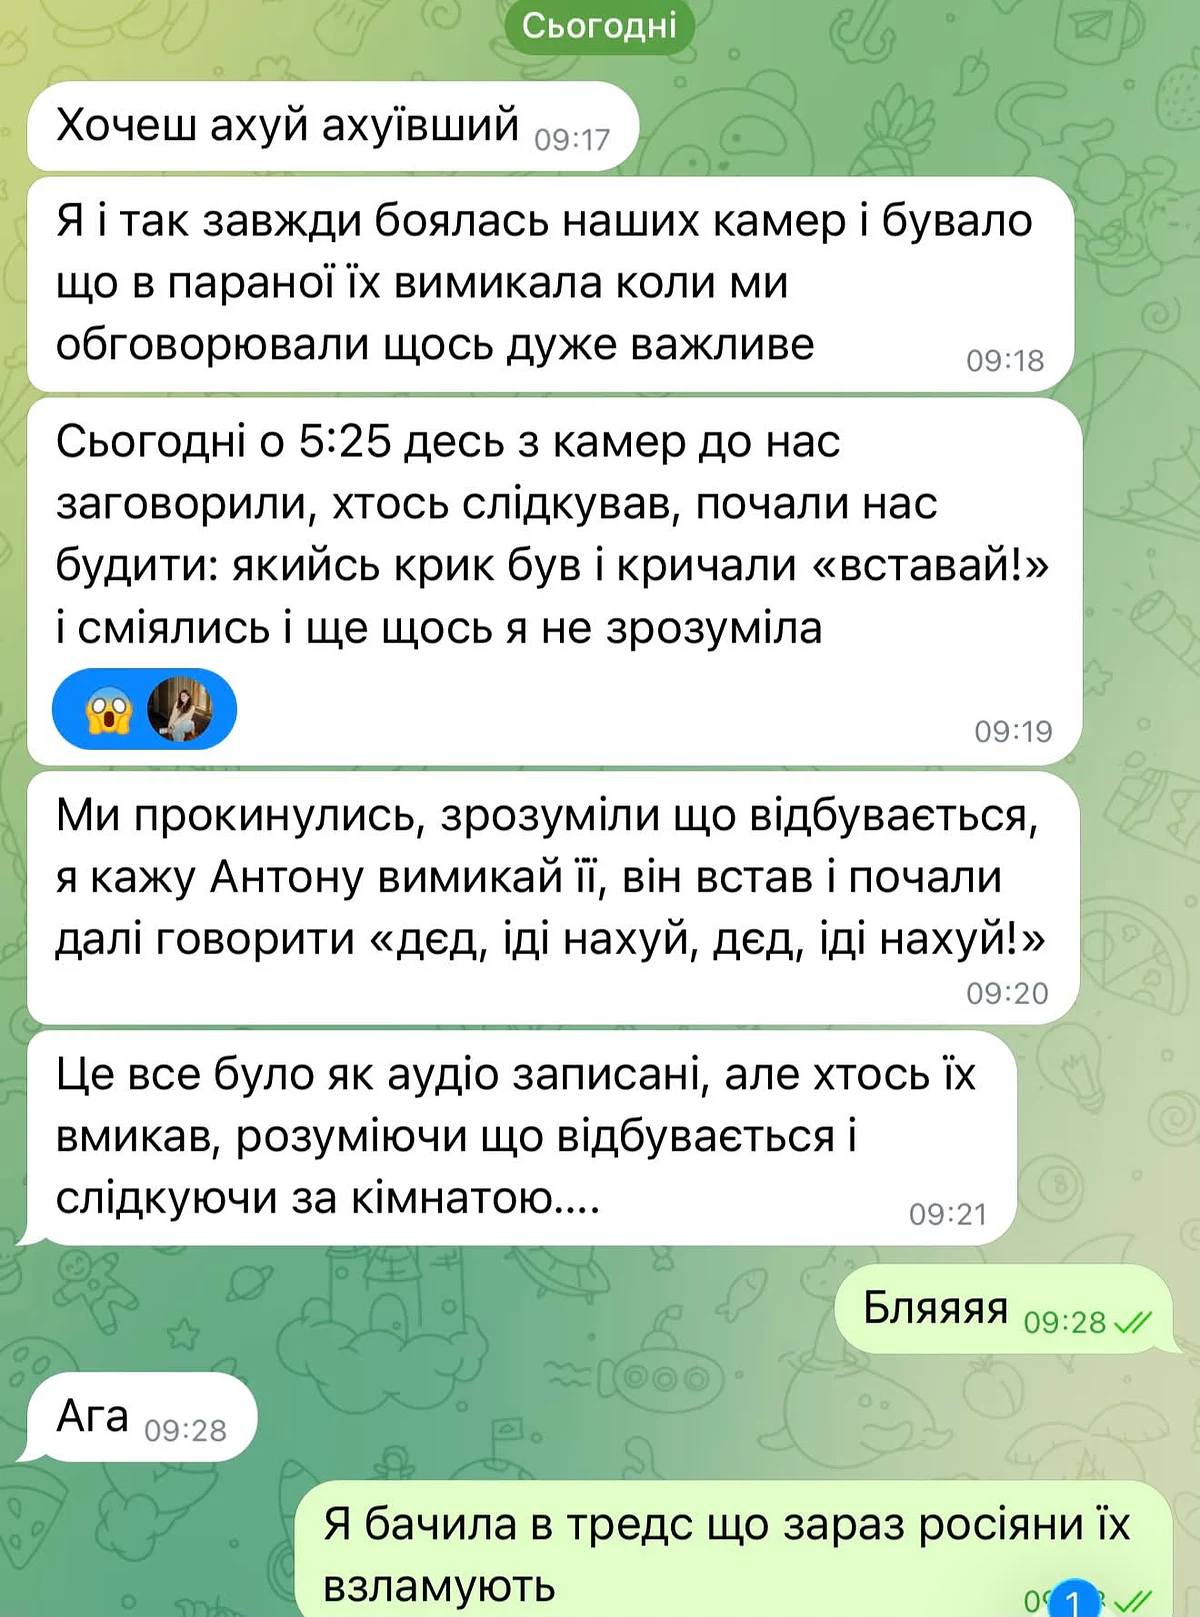
One Threads user shared the story of her sister's camera hack - at around 05:25 in the morning, extraneous voices suddenly began to be heard from the surveillance camera in her apartment. The unknown person, who was watching the room through the lens at that time, began shouting phrases like "get up", trying to wake up the residents. The girl woke up, understood the essence of the situation and immediately asked her husband to disconnect the device from the network. According to her, the DMSS application was used to control this camera, and the SHERIFF security company was responsible for installing and configuring the equipment.
In the comments to this post, it became clear that the case is far from unique. A user with the nickname alexiaferster recalled an incident that happened to her in 2022 or 2023. Then hackers gained access to the camera in the beauty salon where she worked. In the evening, when the woman was cleaning the room, a Muscovite began to address her through the camera speaker, after which he turned on the Russian anthem and a song about "Get up Donbass". The girl simply unplugged the device, ironically wishing the hacker to enjoy how he spent his energy and money on watching the tired woman.
Another user, ngelinalibrik, told an equally disturbing story about a camera that was installed in a room specifically to monitor a sleeping child. One night, the device began to take on a life of its own: the lens moved, and through the app it was visible that someone else was zooming in, zooming out, and turning on the sound. After this incident, the family decided to get rid of the camera altogether.
View in Threads
Official position of the SHERIFF
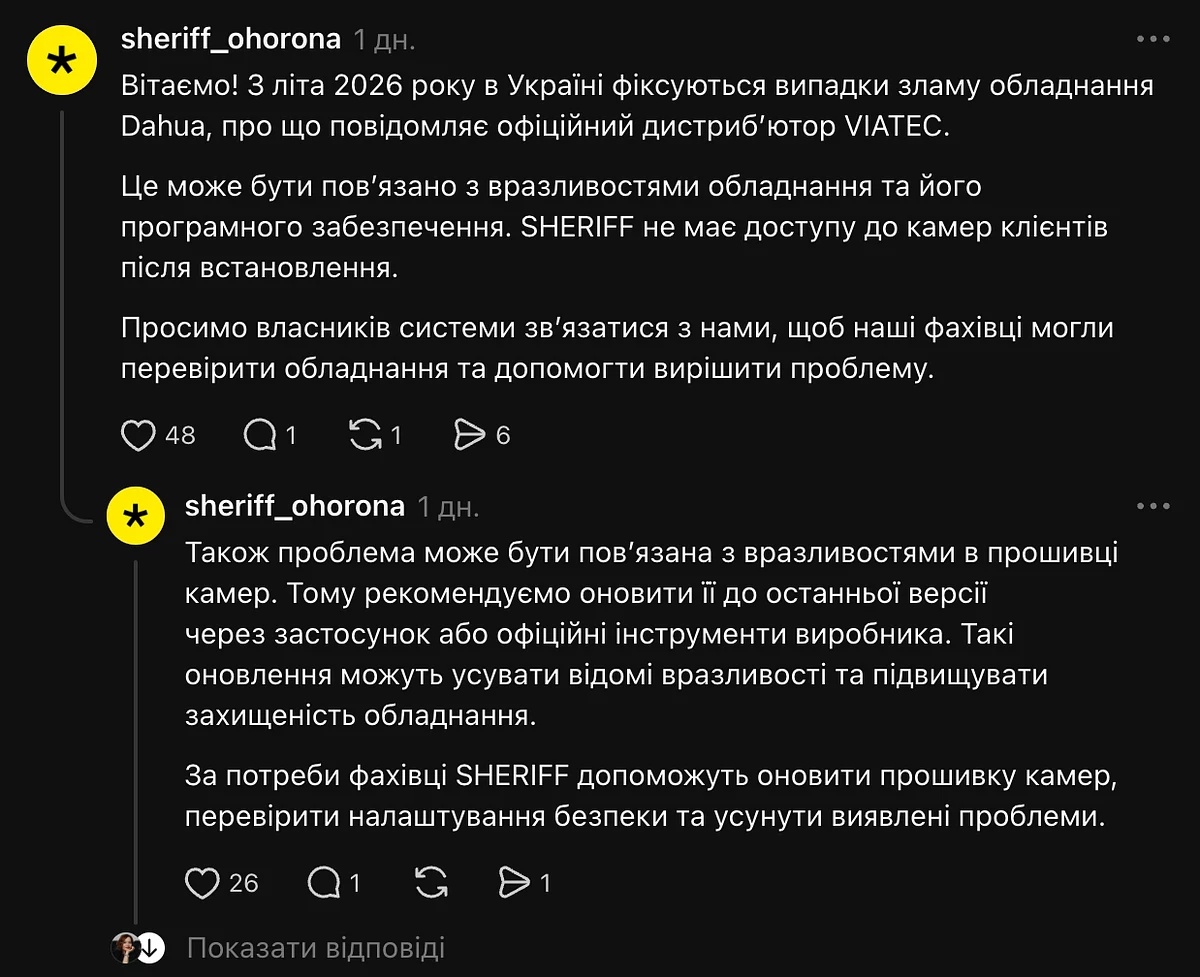
Representatives of the SHERIFF company responded to the post and provided their explanations. The company confirmed the existence of the problem, noting that since the summer of 2026, cases of hacking of Dahua brand equipment have been systematically recorded in Ukraine. The security guards were previously informed about this trend by the official distributor of the equipment, the VIATEC company.
SHERIFF categorically emphasized that after the installation and configuration of the system is completed, they do not have any access to their customers' cameras. The problem lies in the vulnerabilities of the equipment itself and its old software. The security company urged all owners of such systems who have noticed suspicious activity not to hesitate and contact their support service. The company's specialists are ready to help check the security settings, update the firmware to the latest version via the application or official manufacturer's tools, and eliminate the detected threats.
How exactly do hackers penetrate the network?
The official distributor of Dahua equipment in Ukraine, VIATEC, has collected detailed statistics of appeals and, together with the manufacturer, analyzed the technical nature of the hacks. Advice to massively switch to other brands immediately appeared on social networks, but experts explain the situation more prosaically. Dahua is one of the most common brands of video surveillance on the Ukrainian market. Hackers do not choose a specific manufacturer purposefully, but simply scan IP address ranges and cling to any poorly protected equipment. Any other brand with the same huge installed base of devices would have similar hack statistics.
Technical support identifies two main compromise scenarios. The first and most common vector is related to the vulnerability of the old P2P protocol. Dahua has discontinued support for this old implementation along with the outdated SmartPSS application. If the object is still running old firmware with active P2P, an attacker can easily connect to the camera via a cloud service. He does not even need to break through NAT or try passwords. Most often, popular K-series cameras, in particular the K35 model, are affected by this, for which the manufacturer has already released critical updates.
The second vector is absolutely classic for cybersecurity — it is the brute force of weak credentials on devices that the owners have exposed to the open Internet through direct port forwarding. Cameras, DVRs and routers protected by basic passwords of the format admin123, qwerty111 or user123 are found by automated scripts in a matter of minutes. The situation is aggravated by the use of standard access ports, such as TCP 80, 554 or 37777, which hacker scanners check first.
Breakdown statistics and equipment rescue algorithms
According to VIATEC data collected as of the end of October, an analysis of compromised equipment gives a very clear picture. The absolute majority, which is 95% of hacked devices, are equipment over three years old, running on firmware released before 2023. The remaining 5% are relatively new models, whose owners simply never updated the firmware after unboxing.
If the camera has firmware from 2024 or later, hacking through the described vulnerabilities becomes impossible. Accordingly, equipment with old software needs to be updated immediately.
The distributor has developed three clear scenarios for users and installers. If the equipment is older than three years and has already been hacked, you need to download a special firmware with a fix for the problem from the VIATEC FTP server. The manufacturer is constantly updating this list of patches for older models. If the required file is missing, users are advised to contact the technical support form. If the old camera already has an official firmware from 2024, it is enough to simply update to it, since the protective patch is already embedded there by default. For devices younger than three years, the algorithm is even simpler - just update the system to the latest version via the application.
How to build secure video surveillance systems today
To prevent incidents with hackers' nighttime conversations from recurring at new facilities, experts strongly recommend that installers and ordinary users adhere to three ironclad rules of cyber hygiene.
The first rule is to update at the first launch. Before installing and configuring any camera or recorder, you must check the firmware version and, if necessary, immediately update it to the current version of 2024.
The second rule concerns password policy. In today's realities, a password should consist of at least 12 characters and must contain uppercase and lowercase letters, numbers, and special characters. The use of combinations like admin123 should be strictly prohibited even at the stage of setting up test benches.
The third rule covers network and port settings. If the owner absolutely needs remote access to the cameras, the standard external ports must be changed to non-standard values. However, experts call the best and safest solution a complete rejection of direct port forwarding. Instead, it is worth using reliable VPN connections or accessing through secure cloud services and up-to-date mobile applications from the manufacturer.
Previously, the government computer emergency response team of Ukraine CERT-UA, which operates under the State Service for Special Communications, warned about mass cases of unauthorized remote access to Dahua brand video surveillance systems. Recommendations from CERT-UA on camera protection:
Disable P2P/Cloud Access in your device settings if you don't use cloud browsing on a regular basis.
Do not publish cameras on the open internet. For secure remote viewing, set up a VPN connection and restrict access to only authorized IP addresses.
Conduct an account audit: check the user list and disconnect any suspicious or unknown accounts.
Update the firmware: manually download and install the latest software versions from the manufacturer's official website and continue to update them regularly.