Наталя ХандусенкоHot News
28 May 2026, 17:08
2026-05-28
New way of tracking: sites can spy on users by analyzing SSD activity
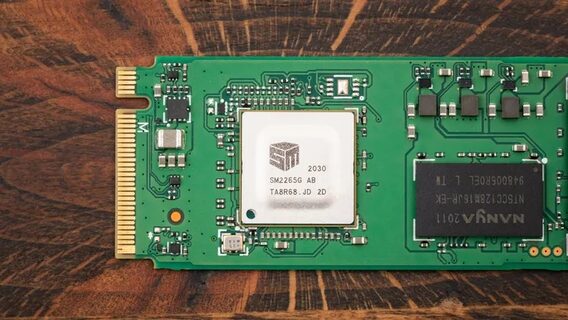
Cybersecurity researchers claim they can spy on browser activity by measuring SSD load via an API. According to them, the FROST attack does not require any permissions or action from the user to determine which applications and websites they are using.
Cybersecurity researchers claim they can spy on browser activity by measuring SSD load via an API. According to them, the FROST attack does not require any permissions or action from the user to determine which applications and websites they are using.
Cybersecurity researchers from Graz University of Technology in Austria have published a paper describing a backdoor attack that allows a malicious website to determine what other sites and applications a visitor has open by measuring the latency of accessing SSDs via JavaScript inside a standard browser sandbox, Tom's Hardware reports .
The technology, called FROST (Fingerprinting Remotely using OPFS-based SSD Timing), was able to identify visited websites with about 89% accuracy and launched applications with about 96% accuracy on a test Mac. The attack requires no action from the victim other than simply visiting the attacker's page, and the attack works across browsers.
FROST uses the Origin Private File System (OPFS), a browser API that allows websites to create and store files on a user's local disk without asking for permission. Previous side-channel attacks on SSDs that have been documented previously required running native code through privileged kernel interfaces, but FROST completely eliminates this need.
The team of researchers reported their findings to Google, Apple, and Mozilla. Google said it did not consider fingerprinting (creating a “digital fingerprint” of a device) a security vulnerability. Apple called the attack “currently outside their remit,” and Mozilla took note of the information but did not implement any fixes.
The attack creates a large OPFS file on the victim's SSD. Both Chrome and Safari allow the website to use up to 60% of the total disk space via OPFS, which is over 150 GB on a 256 GB drive. This file must be larger than the system's available RAM so that each random 4 KB block read is made to the SSD, rather than the operating system's page cache.
When other processes create their own I/O load, it causes noticeable latency spikes when the attacker reads data. These timing patterns are fed into a convolutional neural network that has been trained to recognize specific websites and applications based on their unique I/O signatures.
Because the resource contention occurs at the storage level itself, the attack works regardless of the browser used. Running the attacker's page in Chrome while the victim was browsing in Safari showed a difference in throughput of just 3.38% compared to the attack within the same browser.
A full-fledged fingerprint recognition attack was only tested on an M2 Mac Mini with 8GB of RAM and a 256GB SSD. On Linux, the researchers confirmed the ability to measure SSD latency from a browser, but did not run a full classification for recognition. Windows was not tested at all. In addition, the OPFS file must reside on the same physical SSD drive as the monitored activity, which is not guaranteed on workstations with multiple drives.
Currently, the biggest barrier to this attack is the sheer size of the file: most people will notice tens or hundreds of gigabytes of disk space suddenly disappearing. However, researchers are proposing ways to protect against it, including limiting the maximum size of OPFS files to fit in the system's RAM, or requiring permission requests for OPFS file creation. Since Google does not classify fingerprinting as a security issue, browser-level fixes are unlikely in the near future.
Цікаво, що навіть такі технічні “обхідні шляхи” можуть створювати реальні ризики для користувачів, особливо коли мова йде про непомітне використання дискового простору. Ідея з обмеженням розміру файлів або обов’язковими дозволами виглядає логічною, але трохи тривожно, що браузери можуть не поспішати це виправляти через те, як класифікується проблема. Виходить, що багато залежить від балансу між зручністю та безпекою. top games
Цікаво, що навіть такі технічні “обхідні шляхи” можуть створювати реальні ризики для користувачів, особливо коли мова йде про непомітне використання дискового простору. top game
I honestly cannot remember the last time I found a collection of Car games that kept me entertained for so long. The fact that I can jump between these Car Games so easily is a huge plus.
I honestly cannot remember the last time I found a collection of https://cargames.co
that kept me entertained for so long. The fact that I can jump between these Car Games so easily is a huge plus.
Drive Mad is currently breaking internet records as the most frustratingly addictive driving games. where every single bridge crossing feels like a terrifying engineering disaster waiting to happen.
FROST shows that online privacy still faces unexpected threats, reminding us of the hidden challenges and surprises found in games like level devil - not a troll game, where staying alert is the key to overcoming every obstacle.









Цікаво, що навіть такі технічні “обхідні шляхи” можуть створювати реальні ризики для користувачів, особливо коли мова йде про непомітне використання дискового простору. Ідея з обмеженням розміру файлів або обов’язковими дозволами виглядає логічною, але трохи тривожно, що браузери можуть не поспішати це виправляти через те, як класифікується проблема. Виходить, що багато залежить від балансу між зручністю та безпекою. top games
Цікаво, що навіть такі технічні “обхідні шляхи” можуть створювати реальні ризики для користувачів, особливо коли мова йде про непомітне використання дискового простору. top game
I honestly cannot remember the last time I found a collection of Car games that kept me entertained for so long. The fact that I can jump between these Car Games so easily is a huge plus.
I honestly cannot remember the last time I found a collection of https://cargames.co
that kept me entertained for so long. The fact that I can jump between these Car Games so easily is a huge plus.
honestly cannot remember the last time I found a collection of driving directions kept me entertained for so long
Drive Mad is currently breaking internet records as the most frustratingly addictive driving games. where every single bridge crossing feels like a terrifying engineering disaster waiting to happen.
FROST shows that online privacy still faces unexpected threats, reminding us of the hidden challenges and surprises found in games like level devil - not a troll game, where staying alert is the key to overcoming every obstacle.
Anyone enjoying browser-based entertainment such as slope game should also keep security and privacy in mind.
oh my
players in FNAF 4 rely primarily on a flashlight to defend themselves from animatronics hiding in the surrounding corridors.