"Diya" and banking are downloaded via Viber, and the money disappears in an ATM 500 kilometers away. How new NFC-Relay attacks work in Ukraine
Imagine a familiar scene: a working day, a phone call. The caller introduces himself as a bank security officer or a law enforcement officer and in a worried voice reports a suspicious attempt to withdraw funds from your account. To urgently «block the transaction» or undergo «mandatory authorization via BankID», you are offered to download a special version of «Actions» or an updated bank application. The link comes directly to the messenger.
Imagine a familiar scene: a working day, a phone call. The caller introduces himself as a bank security officer or a law enforcement officer and in a worried voice reports a suspicious attempt to withdraw funds from your account. To urgently «block the transaction» or undergo «mandatory authorization via BankID», you are offered to download a special version of «Actions» or an updated bank application. The link comes directly to the messenger.
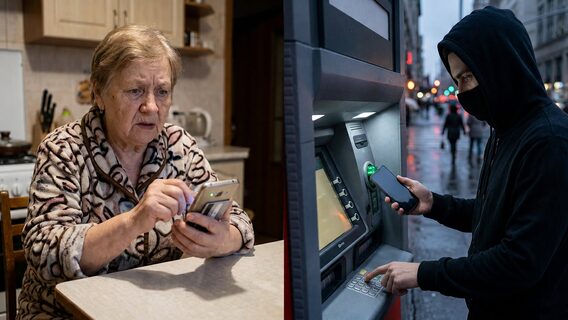
You open the downloaded APK file, see a familiar interface, place your bank card on the back of your smartphone for «reading» and obediently enter your PIN in the formal confirmation window. At that very moment, hundreds of kilometers away, a completely unknown person approaches a street ATM, places his smartphone on the contactless PayPass reader — and the stack of bills taken from the tray becomes the last thing left in your account.
This is not a fiction of cyberpunk writers, but a Card-to-Terminal NFC-Relay attack — a relatively new for Ukraine, but extremely dangerous type of cyberfraud. According to the Ukrainian Interbank Association of Payment Systems Members of EMA, the first similar cases in our country were recorded at the end of 2025, and already in 2026 the scheme turned into a real challenge for the banking sector.
From street taxis in Santiago to ATMs in Bratislava
At its core, a relay attack is a sophisticated transformation of the classic Man-in-the-Middle scheme. Its main and most frightening difference from regular phishing is that attackers don’t even need to steal your digital keys or create a duplicate card. They work with a «live» signal: they intercept and relay the contactless NFC stream between your real plastic and the payment terminal in real time.
European countries faced this epidemic back in 2022. For a long time, the geography of attacks was quite specific — the connection «Great Britain — Uzbekistan» regularly appeared in the reports of cybersecurity specialists. However, over time, the technology became more accessible, and the geography became wider. During 2025 alone, more than 2,600 successful relays were recorded in Britain. Anomaly schemes were recorded in Switzerland, when the card data of Swiss tourists was read directly in Chilean taxis and instantly used for purchases on the other side of the world. And neighboring Slovakia has become one of the hottest spots in Europe, where several such incidents are recorded daily.
At the end of 2025, the first alarm signals appeared in Ukraine. Almost all domestic cases unfold according to the Card-to-Terminal scenario: the intercepted signal ends with either instant cash withdrawal at an ATM or quick payment for expensive goods through a POS terminal.
How digital mosaic works: from call to cash withdrawal
To successfully carry out an attack, fraudsters need a combination of two components: psychological pressure (social engineering) and specialized malware. The latter, by the way, does not even need to be developed from scratch — software like NGate or SuperCard X is openly sold on shadow forums under the «Malware-as-a-Service» model.
The whole drama unfolds in a few seconds:
Psychological hook: A person receives a call or phishing message with a link to a fake resource like diiasupphelpgov.site. They are convincingly explained that to save money, they need to install a «secure module of Diya» or a special version of the banking client.
Camouflage: The downloaded and installed APK file closely copies the familiar design. The user sees the logos of government services, a selection of banks, the authorization screen via the NBU BankID, and the current version number.
Silent trap: The application asks to perform a «simple verification procedure» — to attach a bank card to the back cover of the smartphone and enter a PIN code on the on-screen keyboard.
Relay Magic: As soon as the card chip touches the phone body, the reader captures the transaction APDUs. The malware instantly forwards them via a high-speed WebSocket server to the attacker’s (or his drop partner’s) device, which is standing at the ATM at that very moment.
Finale: The fraudster’s phone goes into Host Card Emulation mode. The ATM sees it as a legitimate plastic card, receives the intercepted chip responses in real time, approves the transaction, and dispenses the money.
The main feature of this scheme is that it is a «live» transaction. The malware works on the principle of a Wi-Fi amplifier: if the physical contact of the card with the smartphone is interrupted even a second early, the chain is broken and the transaction is canceled.
Invisible enemy for defense systems
Why do classic mobile antiviruses and system filters like Google Play Protect often miss such applications? It’s all about their architectural «modesty».
Most traditional banking Trojans behave aggressively and noticeably: they request access to Accessibility Services, try to intercept incoming SMS, draw overlay windows on top of other applications, and download the phone book. Such behavior immediately raises suspicion in security algorithms.
NFC-Relay Trojans, on the other hand, are intentionally designed with the minimum possible set of features. They do not request access to contacts or messages. All they need is a basic permission to work with the NFC module, the ability to keep the network connection active, and permission to prevent the smartphone from going to sleep so that the session does not end at the most crucial moment. To the operating system, such an APK file looks completely innocent, because it does not have the standard signs of Trojan software or remote control programs.
How to protect your own funds and avoid becoming a victim of a scheme. Advice from EMA
Because during a relay attack, the ATM or terminal communicates with your card’s real chip, banks' internal fraud monitors often perceive the transaction as completely legitimate. That’s why your main line of defense remains your own vigilance.
A fundamental rule of digital hygiene is to never install APK files obtained from messengers. No government agency, bank, or charity sends its installation files via Telegram, Viber, or WhatsApp. Any requester who sends a file with the .apk extension for «account protection» or «identity verification» is a scammer. Any applications should be downloaded exclusively from the official Google Play or App Store stores, finding them yourself through a search and checking the developer’s name, number of downloads, and reviews.
In addition, it is important to remember that no bank employee or service center will ever ask you to touch your payment card to your smartphone during a phone conversation to «check NFC» or «activate protection.» You should also not provide your PIN code in third-party applications or show your smartphone screen during calls — this gives fraudsters the opportunity to see your push notifications and details.
If during a conversation you feel the slightest pressure or are persuaded to perform strange manipulations with the phone and card, the best solution would be to immediately end the call. After that, you should call the bank’s hotline yourself at the number printed directly on the back of your payment card and report the incident. And in everyday life, if you rarely use contactless payments from your smartphone, it is better to keep the NFC module turned off in the quick settings menu.