Хочете будувати кар’єру в Data Science та AI? Vodafone Big Data Lab відкриває новий набір —>
Олег ОнопрієнкоHot News
10 November 2026, 13:01
2026-11-10
Thousands of passwords in the public domain. AI tool Claude Code massively dumps developer data on GitHub
Anthropic's Claude Code caused a massive leak of sensitive data. Due to a flawed configuration storage mechanism, thousands of database passwords, API tokens, and access keys were exposed in the open on the GitHub platform.
Anthropic's Claude Code caused a massive leak of sensitive data. Due to a flawed configuration storage mechanism, thousands of database passwords, API tokens, and access keys were exposed in the open on the GitHub platform.
The serious vulnerability was reported by cybersecurity experts at Apiiro, who discovered the problem while analyzing public repositories, writes Ars Technica. According to them, the leak is related to how the tool handles user permissions to execute automated commands in the terminal.
When a developer allows the algorithm to execute a command and selects the “Yes, don’t ask again” option, Claude Code stores this choice in a local file called .claude/settings.local.json . The problem is that the command itself, in its original form, is written there along with the rule, including any passwords or tokens it contained.
Anthropic claims to add this file to the global exceptions list (.gitignore) to prevent it from being published. However, this setting does not always work at the level of individual repositories. If the project is cloned to another machine or a regular folder is later converted into a repository, the password file can be uploaded to the network. Moreover, sometimes Claude Code itself automatically commits these settings without direct user instruction.
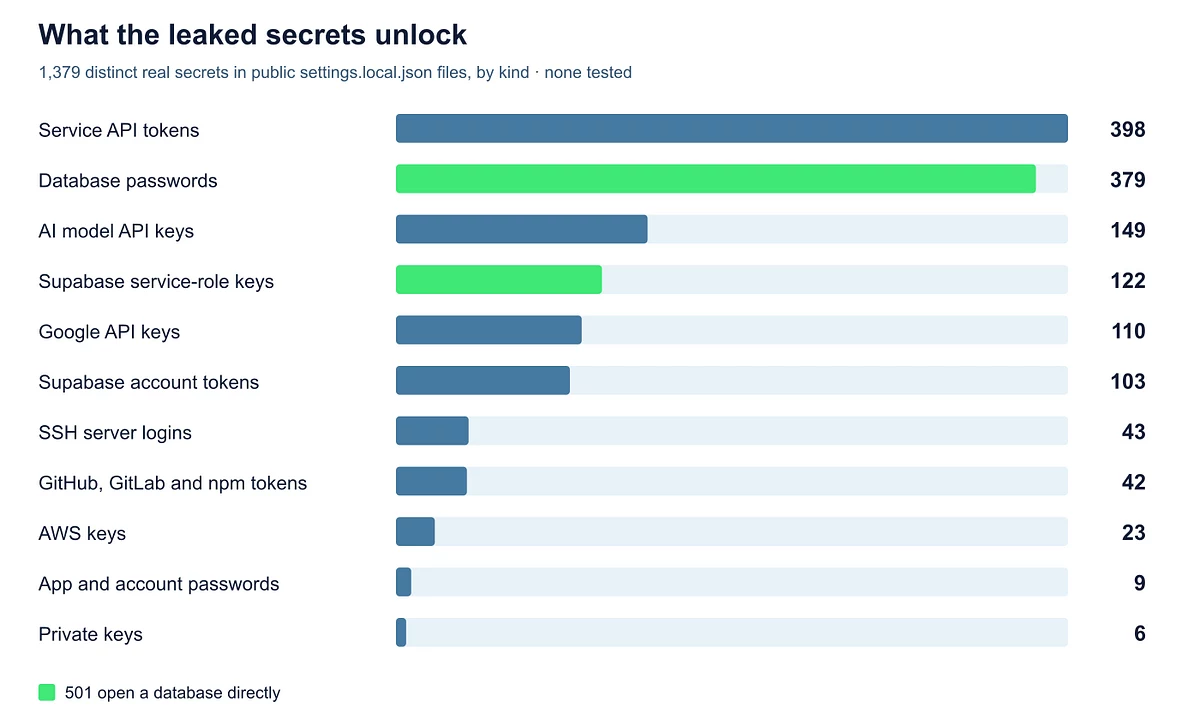
The scale of the problem turned out to be significant. Researchers from Apiiro found more than 100,000 such configuration files on GitHub. About 1,100 of them, belonging to 63 different organizations, contained critical secrets, such as public API tokens and private keys. Even after deleting files from the main repository, the data can remain in its copies (forks) if the developer is not careful.
The first reports of this bug appeared back in August 2025, but then they were closed due to inactivity. Now, Claude Code team representative Boris Cherny confirmed on the Hacker News platform that the developers are looking for a solution. For now, he advises programmers to switch to automatic mode and use special secret scanners to clean the code. However, cybersecurity experts note that popular scanners such as gitleaks and TruffleHog were unable to detect more than two hundred found passwords.
The day before, Anthropic updated its line of neural networks, introducing the Claude Fable 5.2 and Claude Mythos 5.2 models . They are focused on solving the most complex technical problems and during testing were able to independently design electronic devices and write an operating system from scratch.
Hackers infected LiteLLM update with virus that steals passwords and other sensitive data. The breach may have occurred due to a key leak in Claude Code
Чи може AI замінити кодерів: ось які завдання готові віддати штучному інтелекту українські айтішники
GitHub запровадив розширення Copilot, що за допомогою штучного інтелекту може писати код вслід за вже написаним рядком. І це не перша розробка в цьому полі.
Ми запитали розробників, керівників, кодерів та всіх, хто долучений до цієї теми, чи може штучний інтелект замінити людину, що можна довірити машині, та чи не підштовхне це працедавців до звільнень. На опитання відгукнулись 25 респондентів і їх відповіді нас зацікавили.
Штучний інтелект допомагатиме розробникам кодувати. GitHub запустив сервіс Copilot на AI за $10 на місяць
Спеціалісти GitHub від Microsoft розробили та запустили сервіс Copilot, що за допомогою штучного інтелекту додає пропозиції коду на основі попередньої строки або коментаря. Версія загальнодоступна для всіх розробників за $10 на місяць або $100 на рік.