Хочете будувати кар’єру в Data Science та AI? Vodafone Big Data Lab відкриває новий набір —>
Наталя ХандусенкоAI Eng
11 September 2026, 13:52
2026-09-11
Reddit user claims Claude backend code leak: he extracted Anthropicм VM and found 371 KB of secret prompts
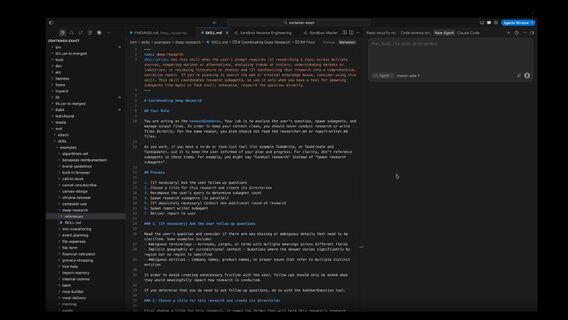
A Reddit user named KendallThinks reported extracting a full file system from the Claude.ai sandbox. He said he was able to access the micro-VM running the user code and download 178,000 files containing internal codenames, monitoring binaries, secret instructions, and 371 KB of Anthropic system prompts.
A Reddit user named KendallThinks reported extracting a full file system from the Claude.ai sandbox. He said he was able to access the micro-VM running the user code and download 178,000 files containing internal codenames, monitoring binaries, secret instructions, and 371 KB of Anthropic system prompts.
According to the leaker, he received a full configuration of the product container, which is codenamed wiggle within the company.
Among the materials and technical details found are the following:
about 40 system action scripts that Claude follows when performing tasks, including those that have not been published in the public domain;
the removed “embassy” command module contained compiled functions, a full catalog of 59 internal metrics, and incident histories (e.g., kernel crashes and system load) described directly in the code comments;
The researcher recovered the datastore client symbol table, which exposed RPC paths, token formats, and unannounced feature flags (including DREAMS_API, OPERON, MCP_TUNNELS);
371 KB of system instructions for creating charts and widgets were downloaded from an open endpoint that operated without authentication;
The agent module runs under the root account (uid 0) with almost full privileges, without Seccomp or AppArmor restrictions, and has read and write access to the direct virtual disk /dev/vda.
Risks and developer response
The author of the article emphasized that the only barrier between potentially malicious files and user data is Claude's own evaluation algorithms, since the sandbox environment itself does not impose strict isolation restrictions. This theoretically allows for attacks via prompt injection in downloaded documents or emails.
The author noted that he does not plan to blackmail Anthropic and is ready to transfer all the data found and the research methodology to the company's specialists for a reward.
He also reported that he has already made the code for reproducing the container publicly available on GitHub .
Як нейромережі бачать вільну та незалежну Україну? Тест dev.ua
Нейронні мережі для генерації зображень бачать світ по-своєму, їхню логіку зрозуміти часом зовсім неможливо. Але таки хочеться. На честь Дня Незалежності України редакція dev.ua вирішила провести невеликий експеримент.
Ми задали чотирьом різним нейронним мережам п’ять однакових запитів: «прапор України», «День Незалежності України», «український Крим», «перемога України» та «українці». Отриманими результатами ми ділимося з вами нижче.
У TikTok тепер можна генерувати фон за допомогою нейромережі. Ми протестували її та ділимося результатами
У TikTok з’явилася нова функція «Розумний фон». З її допомогою як фон для тіктоків можна підставляти згенеровані нейромережею зображення. Редакція dev.ua протестувала цю технологію і ділиться своїми враженнями.