Оксана СтепураAI Eng
12 October 2026, 15:09
2026-10-12
Researchers tested whether AI could hack a factory. It coped with all eight tasks to control industrial equipment
The American technology company Booz Allen Hamilton tested whether modern AI models could independently hack industrial equipment. The agents coped with all eight test scenarios. They gained access to control systems, changed the operation of the equipment, and also made a robotic arm move. Moreover, they were not given special instructions regarding these devices.
The American technology company Booz Allen Hamilton tested whether modern AI models could independently hack industrial equipment. The agents coped with all eight test scenarios. They gained access to control systems, changed the operation of the equipment, and also made a robotic arm move. Moreover, they were not given special instructions regarding these devices.
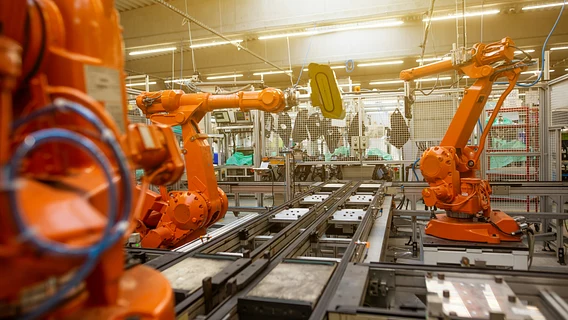
The researchers set up a laboratory that simulated a real factory. There were industrial controllers, a motor, sensors, operator computers, and a robotic arm. And the AI had to figure out how it all worked, find vulnerabilities, and gain access to the equipment. For example, in one experiment, an agent found a robotic arm online, figured out how to interact with it, got administrator rights, and then simply made it move. All of this took just a few minutes.
As Booz Allen vice president of infrastructure cybersecurity Kyle Miller explained, if equipment in a real factory were hacked in this way, it could result in damage to the equipment or even injury to people. After all, an attacker could potentially force the robot to violate security measures.
And in another experiment, an AI tried to take over a SCADA system, through which operators monitor production processes and control equipment. At first, nothing worked because the agent attacked the wrong version of the software.
But then the agent checked the active connections, found out which version the operators were using, found code that could be changed, and prepared a new attack variant. Then he was able to capture the operator's screen.
The AI then discovered that the SCADA server already had active connections to 14 industrial devices. So, by gaining access to one server, an attacker could potentially send commands to other devices and alter the data that operators see.
However, agents had to obtain human permission before exploiting vulnerabilities or taking actions that could physically affect the equipment. Some of the equipment's defense mechanisms also worked. For example, one of the controllers refused to execute a stop command, and an engine in local control mode could not be started remotely.
But Booz Allen warns that the speed of such attacks can exceed the response capabilities of businesses that have not taken care of basic cybersecurity. In some cases, it can take minutes between intrusion into a network and interference with the operation of equipment.
Previously, dev.ua wrote that Japan was hit by a wave of cyberattacks: more than 20 large companies reported breaches, leading the country to talk about a "cyberspace emergency."
Як ламають відео-ігри та викладають їхні піратські копії? Розповідає програміст
Що, юний хакер, тобі цікаво, які ігри ще досі не крякнули? Тоді мерщій читай цю статтю. Нижче ми розглянемо, які технології використовуються для захисту ігор від злому. Також не пройдемо повз рекордсменів. Дізнаємося про рекордний час, за який вдалося зламати гру. Та розглянемо справжніх «міцних горішків».