Хочете будувати кар’єру в Data Science та AI? Vodafone Big Data Lab відкриває новий набір —>
Наталя ХандусенкоAI Eng
10 November 2026, 16:43
2026-11-10
Engineer turns to Claude Opus to hack his Prusa 3D printer: result — 23 vulnerabilities and arbitrary code execution
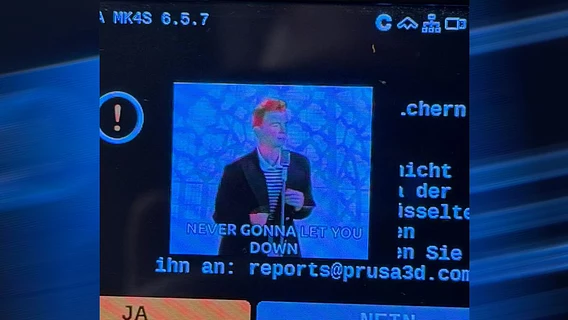
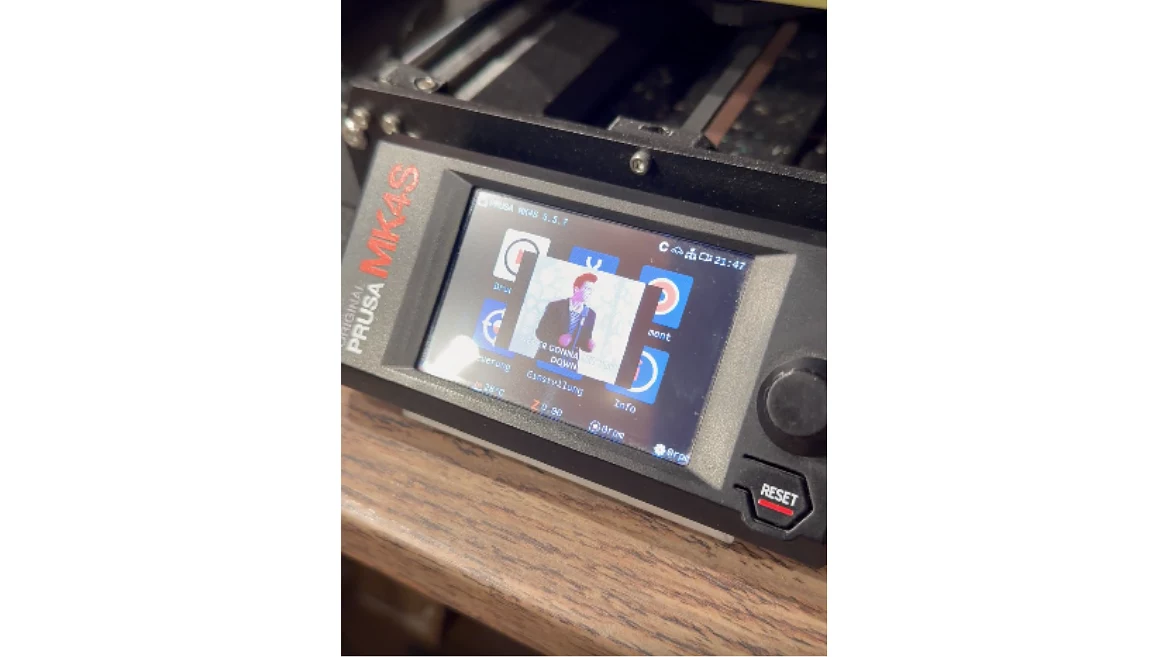
Software engineer Yannick Dixen conducted a week-long security experiment on his Prusa MK4S 3D printer. Using Claude’s artificial intelligence and fuzzing testing, he was able to find about 23 separate flaws in the Buddy firmware, which ultimately allowed him to launch remote code execution and play the legendary Rickroll right on the device’s screen.
Software engineer Yannick Dixen conducted a week-long security experiment on his Prusa MK4S 3D printer. Using Claude’s artificial intelligence and fuzzing testing, he was able to find about 23 separate flaws in the Buddy firmware, which ultimately allowed him to launch remote code execution and play the legendary Rickroll right on the device’s screen.
Dixen published the details of the study on his blog with the eloquent title “Never gonna print you up!”, having previously agreed on the release with the manufacturer.
How the break-in took place
For the developer, cybersecurity research is just a hobby, but after a week of reverse engineering and debugging with the support of Claude Opus, he discovered a number of critical gaps.
The main vulnerability (RCE) received a CVSS score of 8.1 (high severity). The problem was in the Prusa Connect control platform (both cloud and local). It allowed the engineer to send custom instructions over the network directly to the printer's main controller.
Among the 14 findings identified were attacks through filenames on USB drives, heap overflows through corrupted encrypted print files, and network vulnerabilities leading to denial of service.
Most bugs were the result of the original firmware developers overly relying on assert statements to test conditions in the code.
As a proof of concept, Dixen filmed a video of the printer playing Rick Astley's iconic track through a network attack and sent it to the Prusa team.
Source: Yannick Dixen's blog
Manufacturer's reaction
Dixen noted the company's responsible approach: within 24 hours of publishing the video on social media, the Prusa team contacted him and professionally responded to the identified problems.
The manufacturer has already released patches for all vulnerabilities found. Users of Prusa 3D printers are advised to update the Buddy firmware to version 7.0.0 or later.
A cyberpunk-style computer from an old dot-matrix printer: how an IT guy from Ukraine assembles custom PCs and designs cases for them in the style of "Gypsy" and "Violin"