Стас Юрасовздолай шахрая
29 July 2026, 11:00
2026-07-29
Anatomy of a scheme: How an army of "workers" through Viber and Telegram bots devastates Ukrainians' cards on marketplaces
Today’s darknet, unfortunately, offers scammers a ready-made subscription business: they no longer need to write phishing sites themselves, configure the server side, or invent complex communication scripts. All this is taken care of by specialized Telegram bots and ready-made «phishing packs.» The lower level of attackers — the so-called «workers» — only has to find a victim, lure them into the messenger, and drop the link generated by the bot.
Today’s darknet, unfortunately, offers scammers a ready-made subscription business: they no longer need to write phishing sites themselves, configure the server side, or invent complex communication scripts. All this is taken care of by specialized Telegram bots and ready-made «phishing packs.» The lower level of attackers — the so-called «workers» — only has to find a victim, lure them into the messenger, and drop the link generated by the bot.
On average, 1,500 phishing domains under OLX are blocked per month. How does this pipeline work in practice and why do even experienced users give away their own funds? We will understand using a real-life example and analyze the inner mechanics of the scheme together with the Ukrainian Interbank Association of Payment System Members (EMA).
The story of one ad: how the trap works
It all starts with a completely ordinary ad. For example, the daughter of a resident of Svalyava posted a lot of vintage pennants on OLX — she carefully set the price, added a photo, and waited for a buyer. Instead of a real collector, an automatic script, the OLX site parser, came across the ad.
Further events unfolded according to a well-established algorithm, where each step is designed to reduce a person’s vigilance:
Step 1. Exit the «safe perimeter»
The attacker writes not to the internal OLX chat, but directly to Viber. The excuse always sounds convincing: «I don’t receive notifications in the application,» «The internet is slow,» or simply «I’m more comfortable here.» The essence of this maneuver is to deprive the seller of the protection of the marketplace’s automatic filters, which block suspicious links and warn about risks.
Step 2. Legend of paid «OLX Delivery»
The buyer claims that he has already paid for the goods in full through the official OLX Delivery service. But instead of the notification appearing in the seller’s personal account, the attacker sends a link to the messenger: they say, follow it to «confirm the order and receive the money.»
Step 3. Connecting fake «technical support»
When the girl had questions, she was offered «help» — the «OLX technical support» contact on Telegram. The person on the other end of the line, skillfully impersonating an official operator, began to assure her that in order to successfully transfer funds, she needed to complete a «card verification procedure.» The victim was given detailed instructions on how to transfer funds to «confirm the balance.»
Step 4. Debit and quick withdrawal
Under the influence of psychological pressure and convincing arguments from «technical support», the victim independently transfers UAH 48,918.96 from her card. As soon as the money reaches the account of the fake person (the so-called «dropper»), the automatic bot immediately shreds the amount and disperses it further — in particular, a quick transit transfer of UAH 2,999 to another account was recorded to make it difficult for the investigation to find the final recipient.
The police of the Mukachevo Regional Administrative District are investigating criminal proceedings on this fact, and the Svalyavsky District Court of the Transcarpathian Region, by its decision of April 24, 2026, granted investigators access to bank secrets, cash flows, IP addresses, and video recordings from ATMs.
What are the typical schemes for fraud?
For digital fraudsters, the specifics of the site do not matter — it can be the sale of used equipment, branded clothing, or even housing for rent. The main condition for launching schemes is the presence of a chat between users and the ability to simulate the «Secure Transaction» (or delivery) service to replace the original payment page with a phishing clone.
Attackers (in the internal hierarchy, «workers») act according to clear scenarios designed for both buyers and sellers.
Scheme No. 1: Attack on the buyer
Bait: «Worker» publishes an ad for the sale of a popular product at a price significantly below market price.
Switching to a messenger: Under any pretext, the scammer transfers communication from the official marketplace chat to Telegram or Viber.
Imitation of the deal: The buyer is offered to sign up for a «Safe/Safe Deal» and is sent a phishing link where they need to enter their card details for prepayment.
Withdrawal of funds: Instead of freezing money in the service’s escrow account, a regular P2P transfer to the card of the fictitious person («drop») takes place.
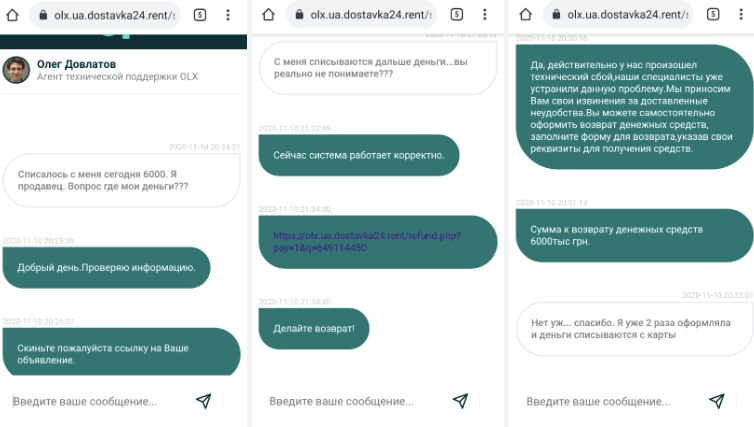
Double-Pay: To double the loot, a «worker» or special operator («dialer») reports a «technical failure» and sends a second link for a «refund.» To get the money back, the victim is required to re-enter all details and confirm the debiting of a similar amount.
Scheme No. 2: Attack on the seller
False prepayment: «Worker» finds an ad from a real seller and assures in the messenger that he is ready to buy the goods right now.
Fake Confirmer: A fraudulent buyer claims to have already paid for the order through «Secure Transaction» and sends the seller a link to a phishing site to «receive money.»
Data theft: On the fake merchant page, they ask the merchant to enter their card details (including CVV) and an SMS confirmation code, supposedly to credit funds. If the victim hesitates, they are sent fake rules of the service or «social engineering» is used.
Postal schemes
A separate layer of attacks is being built around legitimate postal operators. Phishing pages generated through automated Telegram bots completely copy the postal service brand, photo, and price of a specific item:
Postal scheme with the buyer (Scam Seller): Under the pretext of issuing an invoice, the «Worker» learns the buyer’s name and address, after which he sends a link to «pay for delivery and goods.» Then the standard mechanics of stealing funds with a subsequent attempt to write off again due to a «system error» apply.
Postal scheme with the seller (Scam Buyer): The attacker looks for an ad with an open phone number, contacts in the messenger and informs about the registration of postal delivery. The seller is sent a link with the words: «I have already paid for everything, follow the link and collect the money on the card». The result is the entry of payment details on the phishing resource and the emptying of the seller’s account.
Why people believe: psychological and technical traps
Criminals no longer rely on trivial spelling mistakes or crooked fonts. Modern phishing on marketplaces works as a coordinated mechanism:
Complete visual copy. The page the victim lands on completely copies the corporate identity: logos, fonts, and even a card for a specific product with photos and description.
Fake interactive. Fake sites often have a built-in «support chat window» where a bot or real operator instantly answers questions, creating the illusion of solid service.
Manipulation of «bank rules.» Fraudsters often invent non-existent requirements: «Your account must have an amount equal to the cost of the goods so that the bank can verify that the card is active.» This allows you to convince a person to enter data or confirm a debit even when money is being withdrawn from the card instead of credited.
Working after business hours. Running phishing campaigns in the evening, on weekends, or on holidays (when support and security departments are slower).
Here is a real example of a fraudulent message:
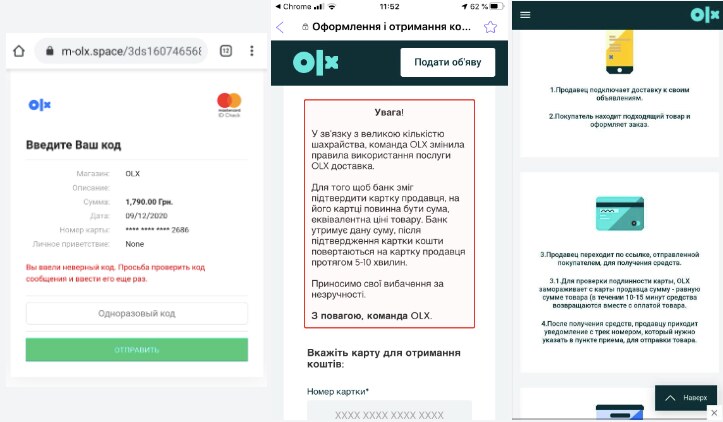
«Due to the large amount of fraud, the OLX team has changed the rules for using the OLX delivery service.
In order for the bank to be able to confirm the seller’s card, there must be an amount on his card equivalent to the price of the goods. The bank holds this amount, after confirming the card, the funds are returned to the seller’s card within 5-10 minutes…»
URL Anatomy: How One Character Exposes Scammers
You can protect yourself from automated phishing if you know the only weak link of the scammers — the domain address. Creating an exact copy of the interface is easy, but registering the official domain of another company is not so easy.
Official addresses: All transactions related to OLX take place exclusively on the olx.ua domain (m.olx.ua for mobile devices or the business page on OLX — name.olx.ua), the company warns. In the new login form, you can also see a redirect to ua.login.olx.com. This is a secure domain that is also owned by OLX.
The domain name must be followed by a slash / (for example, olx.ua/dostavka).
Phishing manipulations: Criminals disguise their sites as official ones using additional words: olx.ua.dostavka24.rent, olx-pay.site, olx.ua.help. This is a clear and fairly clear marker of scammers.
The screenshot shows an example of a fake OLX site. We see the word rent after the last period.
Remember: if the dot at the end of the main name is preceded by anything other than olx.ua, you are on a fraudulent resource.
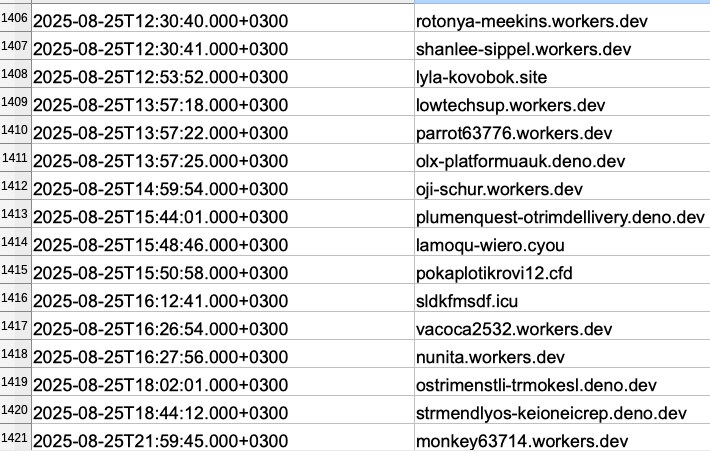
EMA experts also draw attention to a current trend: fraudsters are now much less likely to use olx in their names. In recent years, there has been a change in approaches to the formation of domain names, as well as subdomain names. Registration of sites with «olx» in their names is monitored and sites are blocked even before fraudulent content is uploaded to them. Therefore, domain names such as: verip4ynetdrivecatchboosthub.workers.dev, tineg60775.workers.dev .
Up to 50 such names appear every day.
There are also cases when fraudsters use so-called «aged» domains: they rent and buy back old domains with zero reputation, but with a significant period of existence (to bypass anti-phishing filters).
Security checklist for seller and buyer
To avoid becoming the hero of the next court ruling, EMA experts advise following simple rules of digital hygiene:
Stay within the platform. Discuss the details of the deal only in the internal OLX chat. If the person insists on switching to Viber, Telegram, or WhatsApp, this is a reason to stop communicating.
Don’t look for a link to receive money. There are no separate links for crediting money to the seller on OLX Delivery. Money for the sold item is credited to the card you specified in your personal profile when creating an ad or confirming the transaction in the application.
Check the status only in your account. The real information about the purchase, cancellation or payment is displayed only in the «OLX Delivery» tab in your account.
How to do it: If you received a link to complete a transaction with OLX Delivery or to receive money, enter the full link address (including https://) and check if it is a real OLX site. If the result is green, the site is real, if red, it is a phishing attempt!
Do not give your full details to anyone. To transfer funds, the buyer only needs the 16-digit card number. Expiration date, CVV/CVC code, SMS passwords, and current account balance are private information that should not be entered anywhere except on secure acquiring pages during your own purchases.
Also, do not leave your banking logins/passwords on OLX links!
If you still entered data on a suspicious site, immediately block the card through the banking app, call the bank’s hotline to cancel transactions, and contact the Cyber Police.
And finally: if you’re still not confident in your knowledge of OLX scams, play a game and defeat the scammer with your own intelligence.
Як ламають відео-ігри та викладають їхні піратські копії? Розповідає програміст
Що, юний хакер, тобі цікаво, які ігри ще досі не крякнули? Тоді мерщій читай цю статтю. Нижче ми розглянемо, які технології використовуються для захисту ігор від злому. Також не пройдемо повз рекордсменів. Дізнаємося про рекордний час, за який вдалося зламати гру. Та розглянемо справжніх «міцних горішків».