Наталя ХандусенкоHot News
17 September 2026, 11:26
2026-09-17
"They wanted to hack me through LinkedIn. And very qualitatively." How scammers tried to hack the laptop of the founder of NeedmyLink through a fake Zoom
Fraud attempts on professional networks are becoming increasingly sophisticated. Last week, Yevhen Gumenyuk, CEO and founder of SEO agency NeedmyLink, faced a well-planned attack via LinkedIn. The attackers used fake video conferencing services and tried to gain access to his device via a terminal.
Fraud attempts on professional networks are becoming increasingly sophisticated. Last week, Yevhen Gumenyuk, CEO and founder of SEO agency NeedmyLink, faced a well-planned attack via LinkedIn. The attackers used fake video conferencing services and tried to gain access to his device via a terminal.
The story began with a standard message about cooperation. According to Yevhen, he rarely participates in initial calls with potential clients, delegating this to management, but this time he decided to talk in person.
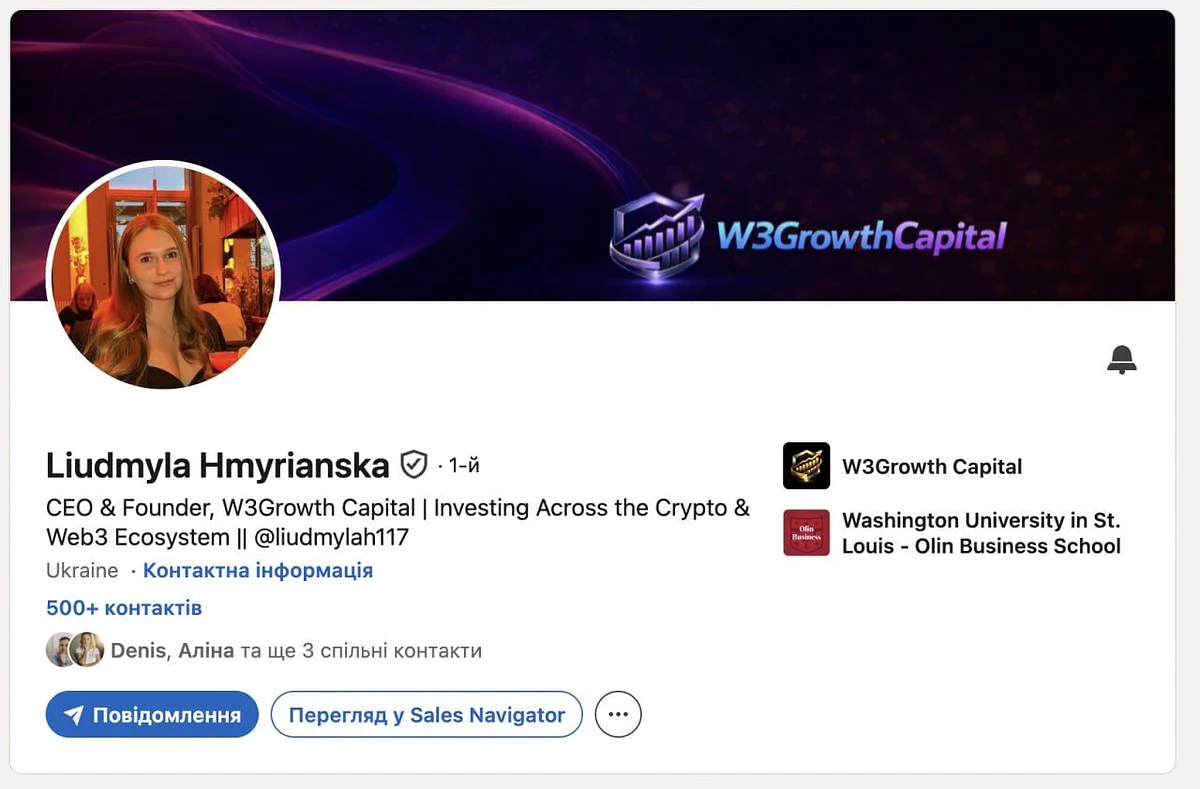
“If I go out on my own, it’s usually large projects and directly with owners. A girl writes. Normal profile, 500+ contacts, there are mutual friends, verified. In the profile — owner of web3/crypto-platform. Writes about a partnership, like they will transfer their clients to us for SEO,” says Yevhen Gumenyuk.
The company's website and the person's profile didn't immediately arouse suspicion, although the resource lacked traffic. Since the agency already had successful experience working with clients in the Web3 and crypto projects worth five-figure dollars, the founder of NeedmyLink agreed to a meeting and reserved a time through Calendly.
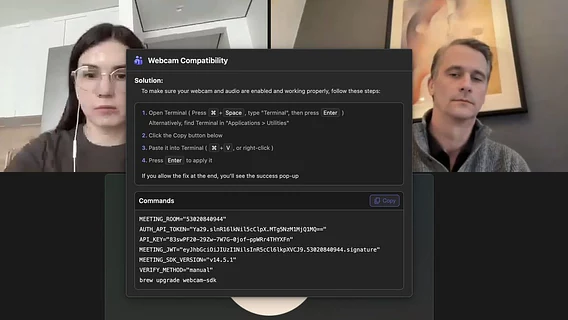
The problems started right away when connecting to the call. The first attempt was made via Microsoft Teams: two people were already waiting at the meeting, but Yevhen's camera and microphone were not working. Instead, a system message appeared on the screen asking for permissions via the terminal.
Assessing the situation as a failure, Yevhen suggested changing the platform, after which he was sent a new Zoom link. However, the scenario repeated itself.
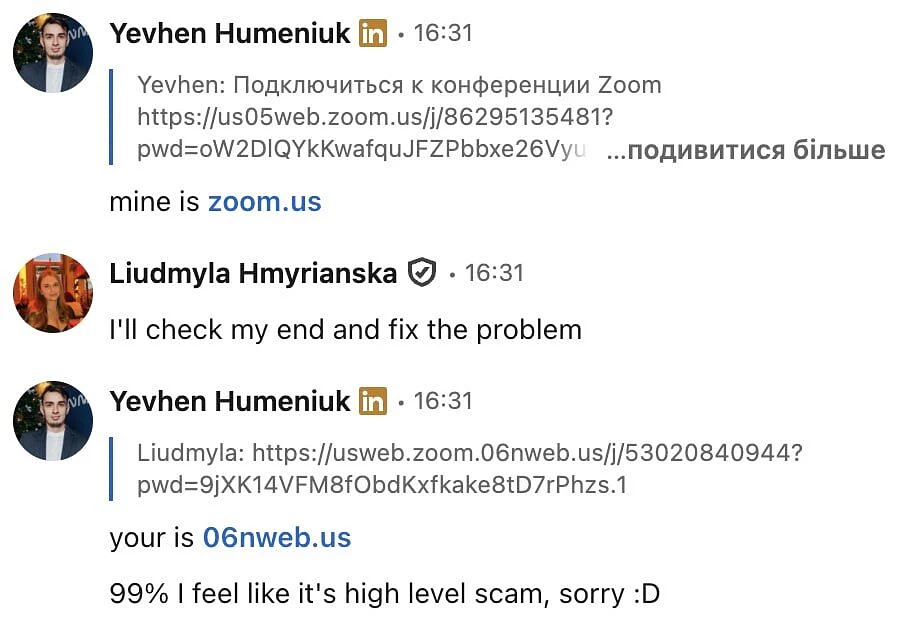
"I go in - the same topic. And the girl also says: "This is my first time doing this, you do it, we'll wait." I check the link, because I was tempted to do it at first, and I realize that Zoom is fake. The funny thing is that before that I had already automatically clicked on the camera permission in Teams," says the CEO of NeedmyLink.
After thoroughly checking the laptop for malware, Yevhen was convinced that the attack was unsuccessful, because the main task of the scammers was to force the user to execute commands in the terminal.
"Of course, if you are asked to open a terminal and register something there, it is already clear that it is a scam. But what struck me was the level of preparation leading up to this moment," the entrepreneur concluded.
Cybersecurity experts remind you: no official video conferencing service (Zoom, Teams, or Google Meet) requires you to enter commands via a console or terminal to grant access to your microphone or camera. Always check link URLs before clicking.
A recruiter received dozens of very similar messages — supposedly from “candidates” — in just 10 minutes. What are these — bots, scammers, or automation — the community is wondering
LinkedIn заблокував пост айтішника «за булінг та харасмент». Раніше він поскаржився в підтримку на іншого користувача, що звинуватив українську IT-компанію у нацизмі
"CEO та засновник SEO-агенції NeedmyLink Євген Гуменюк"
хотів показати який крутий перемовник, а по суті обісрався. Давайте по чесному:
"web3/crypto-платформи" - редфлаг №1.
" Пише щодо партнерства, типу вони будуть передавати нам своїх клієнтів на SEO" - швидка вигода, редфлаг №2.
"Сайт компанії та профіль співрозмовниці не викликали миттєвих підозр, хоча ресурсу й бракувало трафіку" - типові помилки типових керівників.
Перевірити трафік він зумів, а на URL звісно забив. Ну ж типовий керівник.
"Натомість на екрані з’явилося системне повідомлення з проханням надати дозволи через термінал." - це вже наслідки.
І оце:
"Експерти з кібербезпеки нагадують: жоден офіційний сервіс відеоконференцій (Zoom, Teams чи Google Meet) не вимагає введення команд через консоль або термінал для надання доступу до мікрофона чи камери." - то якісь погані експерти. Всі програми при першому запуску питають ці дозволи, і якщо запускати через браузер - аналогічно. Повторні запити залежать від того яку опцію обрали попереднього разу...










"CEO та засновник SEO-агенції NeedmyLink Євген Гуменюк"
хотів показати який крутий перемовник, а по суті обісрався. Давайте по чесному:
"web3/crypto-платформи" - редфлаг №1. " Пише щодо партнерства, типу вони будуть передавати нам своїх клієнтів на SEO" - швидка вигода, редфлаг №2. "Сайт компанії та профіль співрозмовниці не викликали миттєвих підозр, хоча ресурсу й бракувало трафіку" - типові помилки типових керівників. Перевірити трафік він зумів, а на URL звісно забив. Ну ж типовий керівник. "Натомість на екрані з’явилося системне повідомлення з проханням надати дозволи через термінал." - це вже наслідки.
І оце:
"Експерти з кібербезпеки нагадують: жоден офіційний сервіс відеоконференцій (Zoom, Teams чи Google Meet) не вимагає введення команд через консоль або термінал для надання доступу до мікрофона чи камери." - то якісь погані експерти. Всі програми при першому запуску питають ці дозволи, і якщо запускати через браузер - аналогічно. Повторні запити залежать від того яку опцію обрали попереднього разу...
Сам винуватий що з расіянами на контакт пішов, це видно з расіянських написів на скріншотах.
Сам винуватий що з расіянами на контакт пішов, це видно з расіянських написів на скріншотах.